
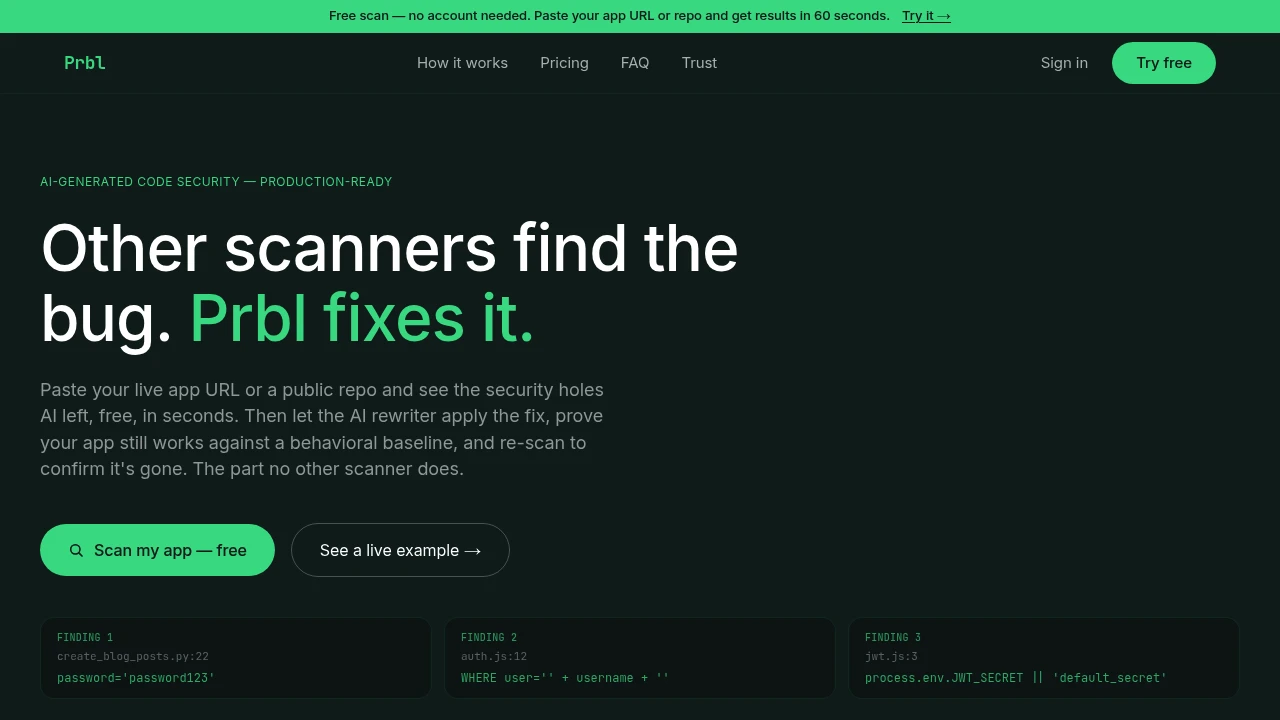
Prbl is a free security scanner for code that came from AI tools. It’s for developers who already run general scanners but still worry about the specific kinds of bugs AI assistants tend to introduce (secrets, missing auth checks, injection patterns, weak crypto). You can paste a live app URL or a public repo and get file and line-level findings without creating an account.
Prbl’s key difference is the closed loop. Many scanners point out problems but don’t address the part that breaks teams: fixing the issue without damaging the feature around it. Prbl captures a baseline of what the relevant code does first, applies the fix as a clean diff you can approve, then verifies by re-scanning that the original security gap is no longer present.
The types of issues it calls out are the patterns teams see in AI-generated or edited code. Examples from its material include hardcoded credentials, string-concatenation injection, fallback secrets in environment variable lookups (like a JWT secret defaulting when the env var is missing), and timing-unsafe webhook signature checks. It also emphasizes a security gap that general SAST tools often miss: routes that work but omit authentication or authorization checks.
If your goal is to find and remediate the common failure modes in AI-written code, Prbl fits best. It doesn’t position itself as a replacement for existing scanners, so it’s geared for teams that want an extra layer focused on AI-code mistakes.


